Login to profile

CREST Accredited Teams (Government)

Non-commercial cybersecurity functions such as a SOC team or an in-house incident response capability within a central government department, can gain CREST accreditation, providing independent assurance that your team meets a rigorous and consistent standard.

Who is this for?

This accreditation route is intended for any team, business unit, department, function, centre of excellence or shared service that delivers cybersecurity services within government – and that is not a commercial cybersecurity service provider.

Why become a CREST Accredited Government Team

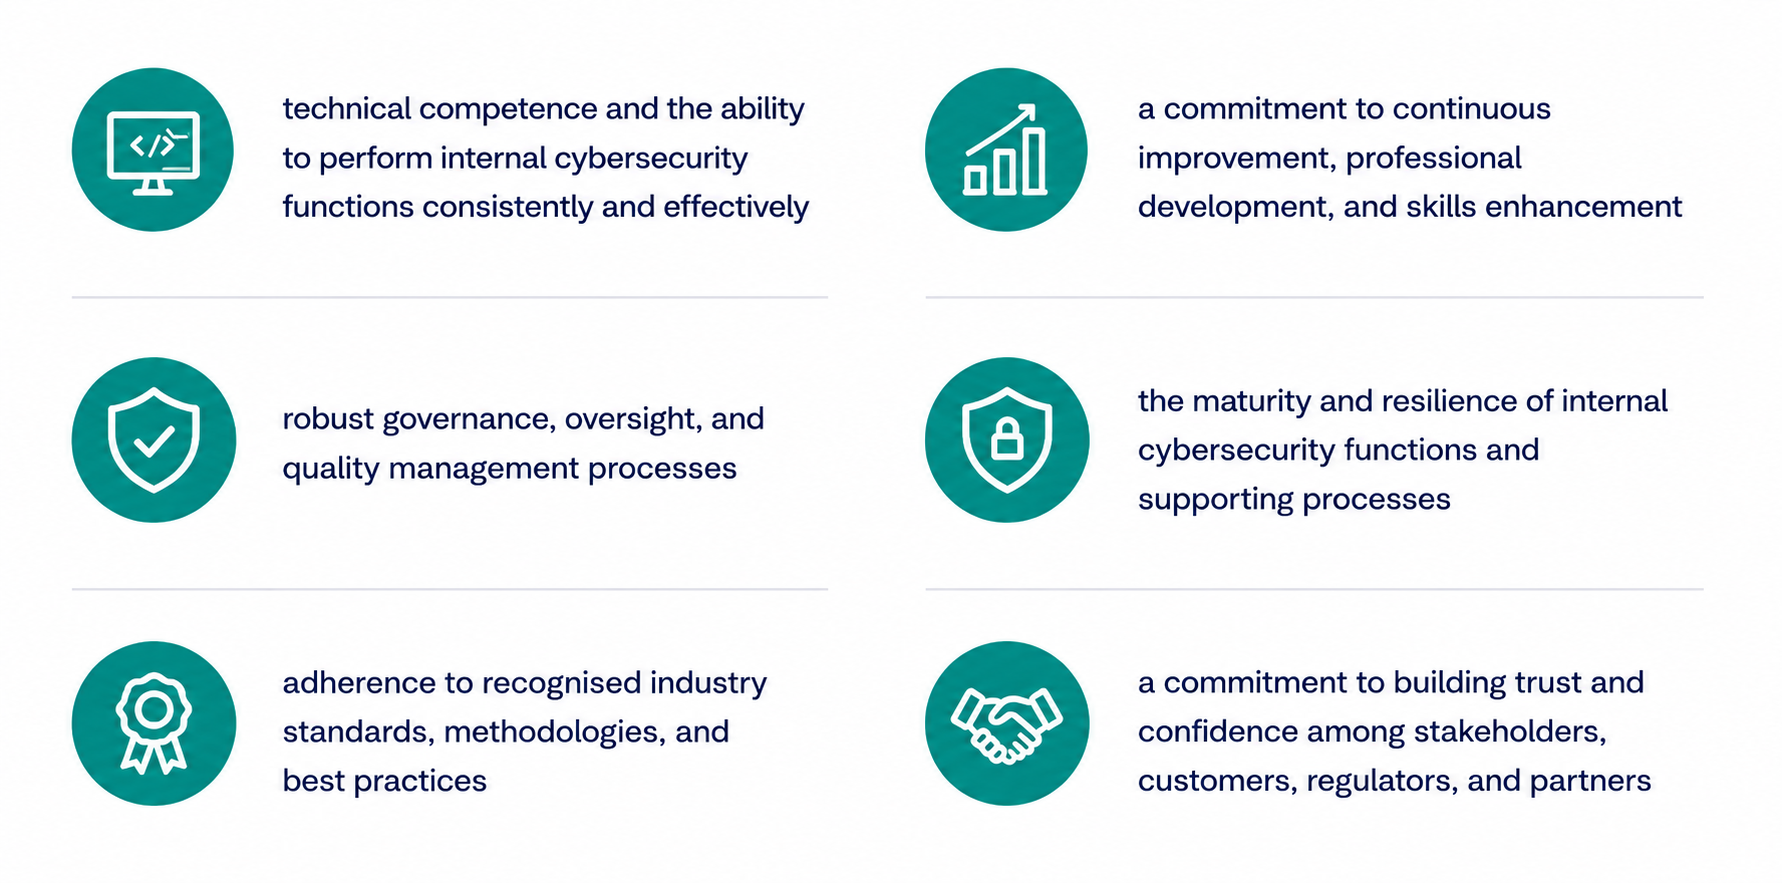
Accreditation signals to regulators, auditors, boards and oversight bodies that your internal capability meets a benchmark equivalent to the best in the industry. It also demonstrates:


How do CREST standards apply to government teams?

The guidance may be applied to service areas including, but not limited to:

  • penetration testing;
  • security operations centre services;
  • cyber threat intelligence;
  • incident response;
  • vulnerability assessment;
  • security architecture;
  • incident exercising;
  • other CREST-accredited services where the service is delivered internally.

What evidence does CREST look for in accrediting government accredited teams?

The standard does not change, only how some evidence is provided. For example, corporate insurance arrangements satisfy commercial insurance requirements.

Internal governance, corporate policies, internal customers and shared functions are all valid evidence. CREST guidance explains how each requirement translates to an internal context.