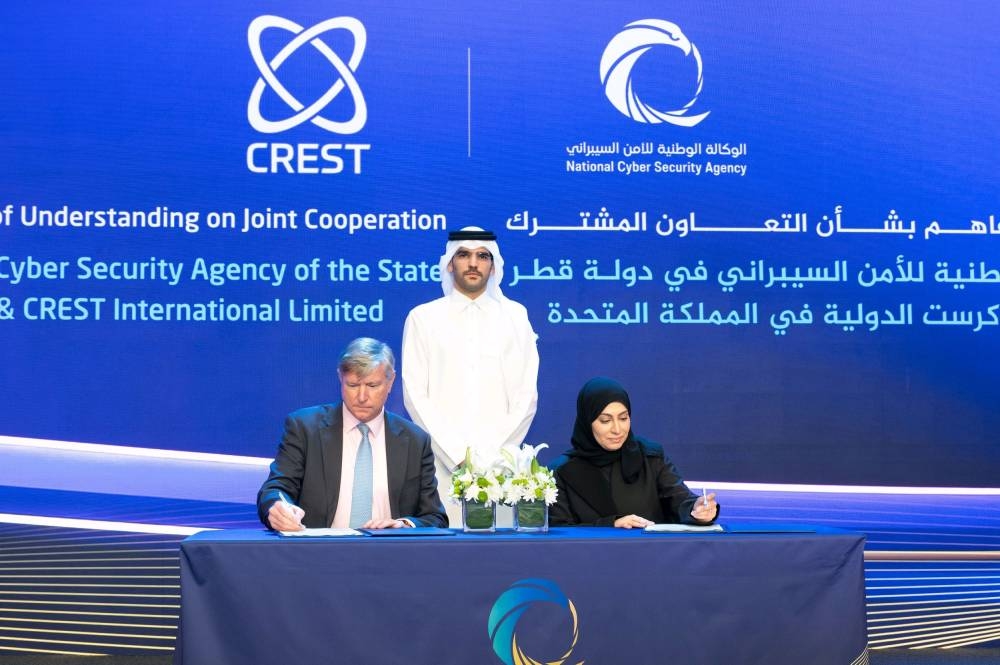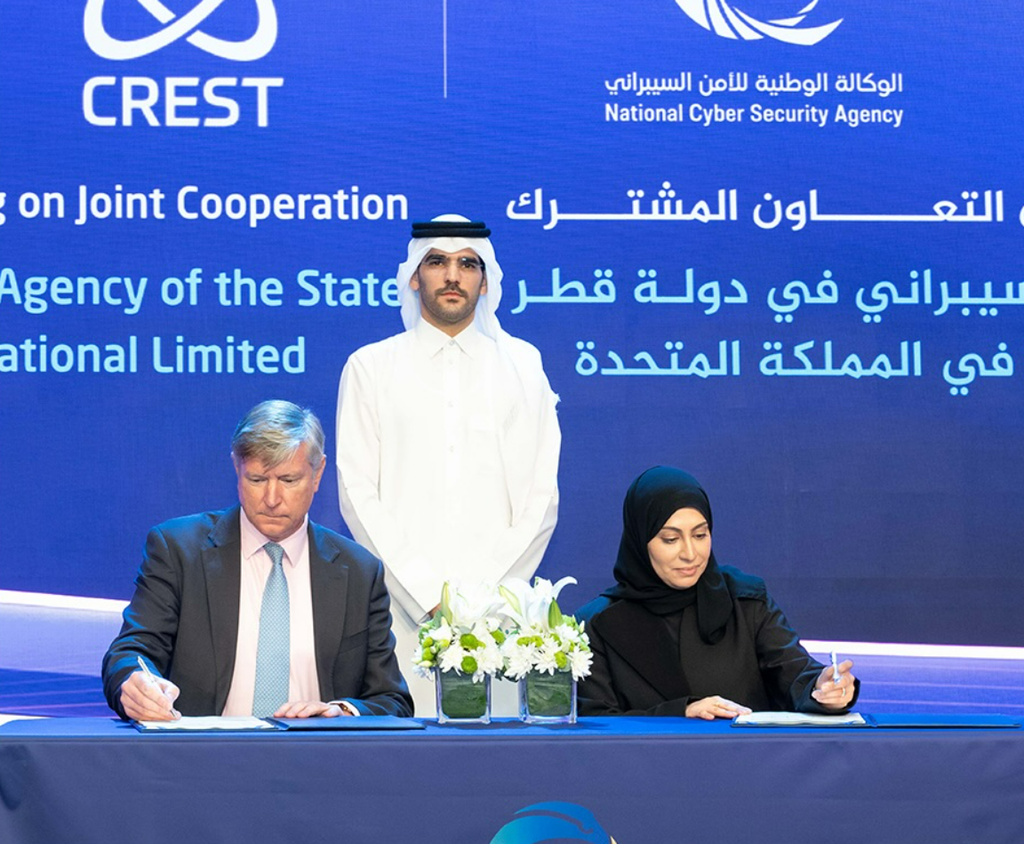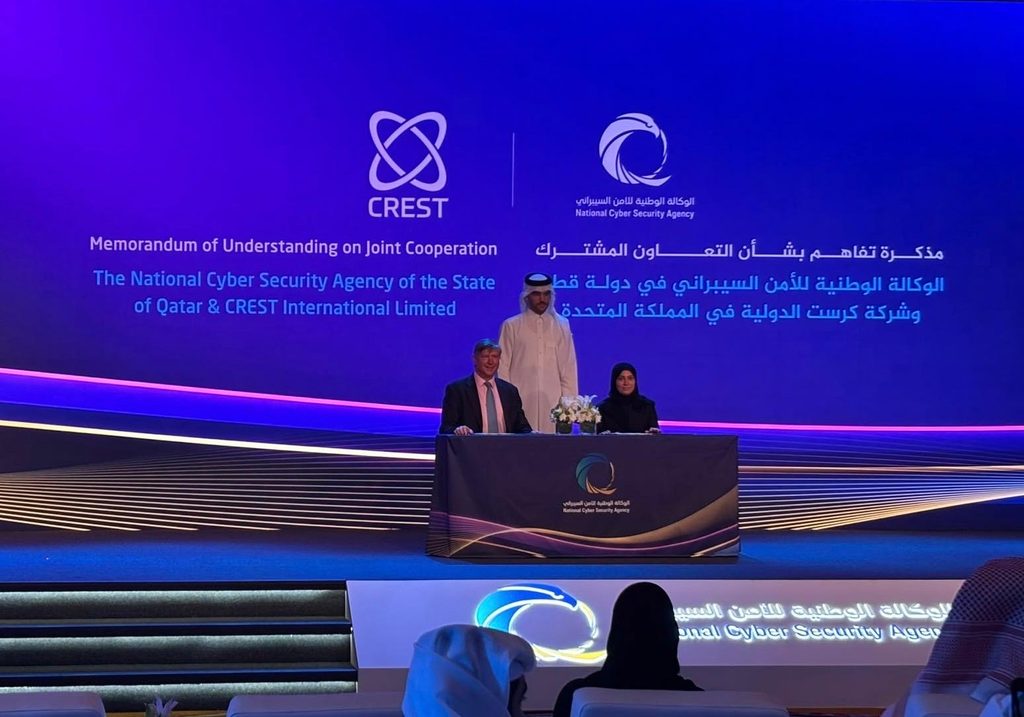
New MOU further aligns penetration testing accreditation, reduces duplication for service providers and creates easier routes into the Qatari and international markets.
The agreement builds on a partnership that began with the signing of the organisations’ original MOU in 2022. Since then, CREST and NCSA have worked to align their respective approaches to penetration testing accreditation, with NCSA becoming a CREST Government Supporter in 2024. Eight Qatari companies also participated in a CREST Cyber Accelerated Maturity Programme (CREST CAMP), receiving access to CREST Pathway and mentoring from CREST members. One participating company subsequently achieved CREST accreditation and membership.
The new MOU further aligns the requirements, standards and accreditation methodologies used by CREST and NCSA.
It recognises that a substantial proportion of the evidence, documentation and improvement work completed by a service provider for one accreditation route may also be applicable to the other. This is designed to reduce the time, cost and duplicated effort involved for organisations seeking recognition from both CREST and NCSA.
Sebastian Madden, Chief Product Officer, CREST International, said:
“Our collaboration with NCSA shows what can be achieved when assurance bodies align around a shared commitment to quality. This new MOU further aligns our approaches to penetration testing accreditation, reducing duplicated effort for service providers while maintaining robust standards.
“It also creates practical opportunities in both directions: supporting NCSA-accredited providers on their journey towards CREST accreditation and giving CREST members a more accessible route into the Qatari market. We believe this provides a strong model for how international collaboration can build trust, strengthen cyber resilience and reduce unnecessary barriers to trade.”
The agreement is intended to deliver benefits across the cybersecurity ecosystem: consistent international standards for service providers operating in Qatar, easier capability development for Qatari providers, greater market access for CREST members and increased choice for buyers of cybersecurity services. The collaboration is also being positioned as a model for how regulators and assurance bodies can reduce friction in cross-border trade while maintaining quality.
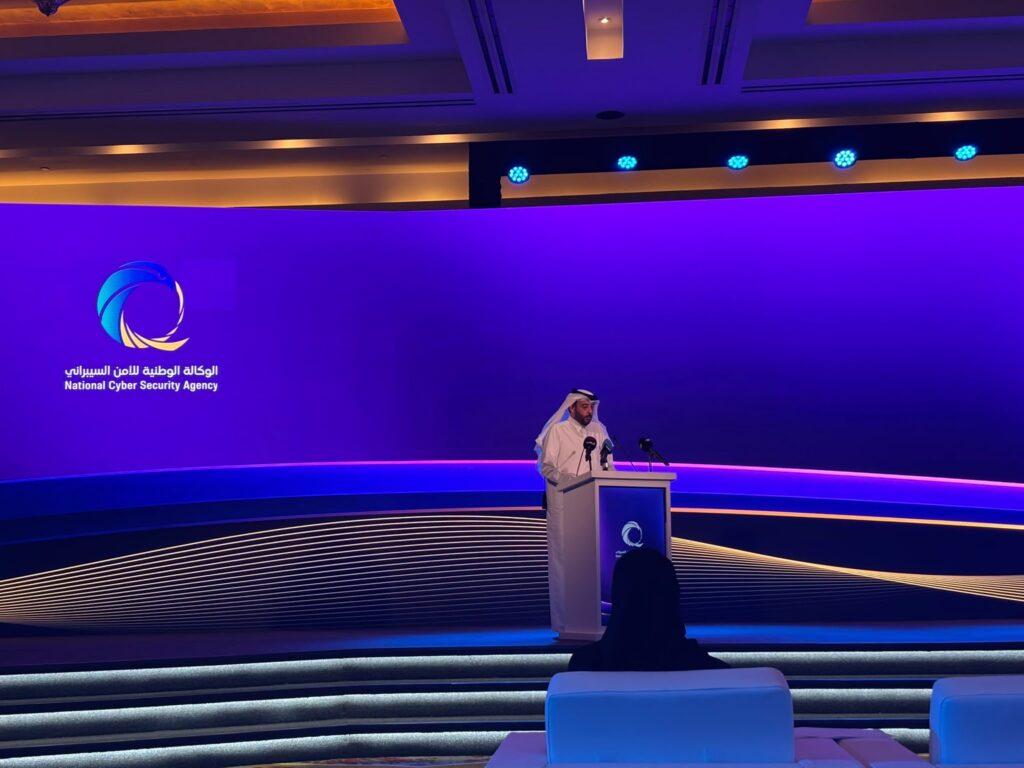
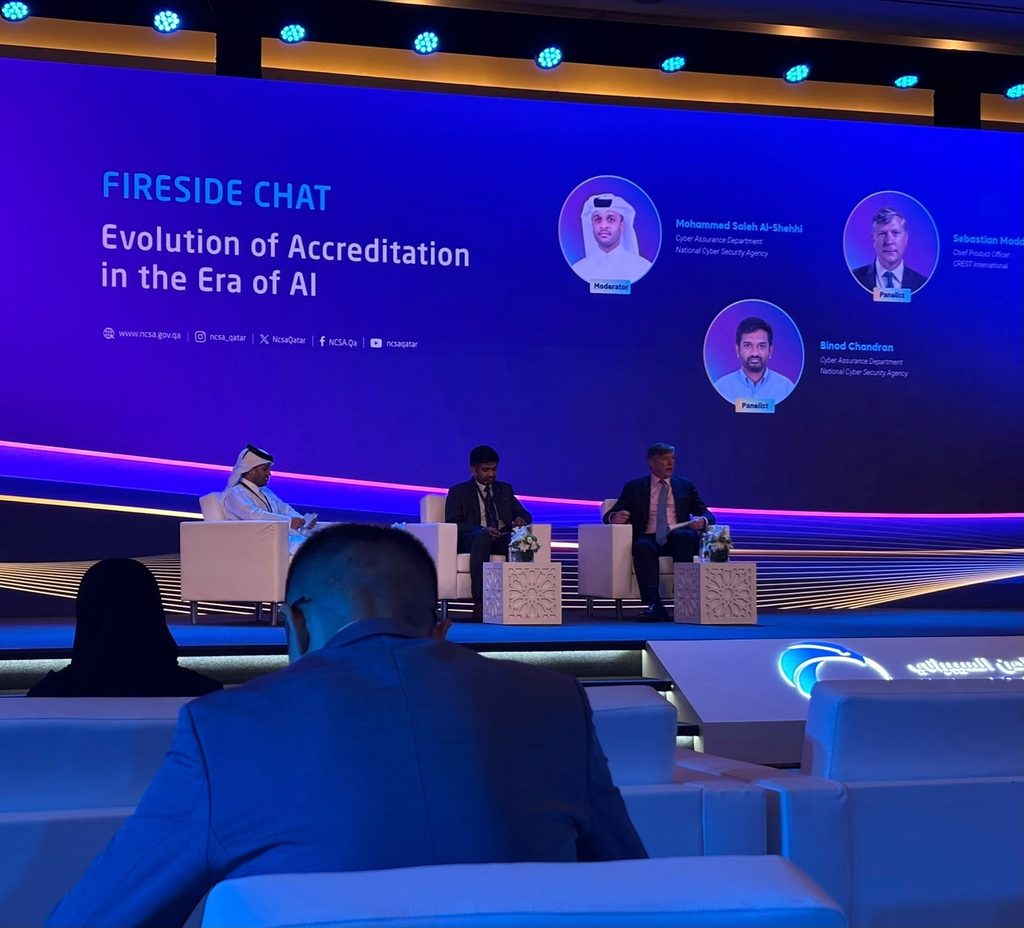
The MOU was signed at the Cyber Assurance Conference 2026 in Qatar on 5 October, where Madden presented “Building trust, opening markets: A new model for Cyber Assurance”, examining how the two organisations are reducing barriers and expanding opportunities for trusted providers.